Perpetual Due Diligence for Fund Managers
Monitoring Portfolio Companies, Counterparties and Service Providers Between Reviews
Quick answer
Perpetual due diligence for fund managers is continuous, trigger-based monitoring of the portfolio companies, deal counterparties, co-investors and fund service providers a manager depends on, with an investigation and a recorded decision each time a defined risk event occurs.
It applies the logic of perpetual KYC to relationships beyond the investor file. Typical triggers include sanctions designations, ownership and key-person changes, enforcement actions, litigation and credible adverse media. The output is an audit trail that answers SEC examiners, CIMA-mandated auditors and LPs.
Key takeaways
- Cayman’s new CIMA AML Rule and Sanctions Rule came into force on 18 September 2026. Under them, outsourcing an AML function does not transfer accountability, and the independent AML audit must cover third-party relationships and outsourcing.[1]
- The SEC’s amended Regulation S-P requires written policies for overseeing service providers that access customer information. Larger advisers had to comply from 3 December 2025 and smaller advisers from 3 June 2026.[2]
- EY found that 58% of surveyed asset managers still run KYC reviews on a fixed 1, 3 or 5-year cycle, and 42% outsource onboarding and KYC to third parties (EY, 2024).[3]
- FinCEN has postponed its investment adviser AML/CFT rule to 1 January 2028. Investor KYC obligations are on a horizon, but third-party and portfolio exposures exist today.[4]
- A calendar review records what was true on the review date. Perpetual due diligence records what changed since, and what the firm did about it.
What is perpetual due diligence for fund managers?
Perpetual due diligence is the practice of keeping risk assessments on a fund’s external relationships current between scheduled reviews. Instead of waiting 12 or 36 months to look again, the manager monitors each relationship continuously and opens a review when a defined event occurs.
The mechanism is the same one banks call perpetual KYC (pKYC): event-driven review instead of calendar review. The difference is scope. Perpetual KYC is usually discussed for investors and customers. Perpetual due diligence covers the relationships that carry a fund manager’s investment, operational and reputational risk after the subscription documents are signed.
Trigger event: a change in a counterparty’s ownership, management, legal, regulatory, sanctions or media profile that is material enough to require a documented reassessment before the next scheduled review.
Investor KYC is one of four monitoring duties
Most perpetual KYC content stops at the investor. For a fund manager, investors are often the best-documented relationship, because a fund administrator already holds the file. The less-watched exposures sit elsewhere.
| Relationship | Who usually watches it | What goes wrong between reviews |
|---|---|---|
| Investors and LPs | Fund administrator, investor services | Change of UBO, PEP status or sanctions exposure after onboarding |
| Portfolio companies and management teams | Deal team, board representatives | Executive misconduct, litigation, regulatory action, a sanctioned customer or supplier |
| Deal counterparties and co-investors | Often nobody after closing | A co-investor’s backer is designated, or a seller faces fraud allegations post-close |
| Fund service providers and delegates | Operations, procured once and renewed | Administrator, placement agent or distributor faces enforcement, ownership change or a data breach |
The fourth row carries most of the live regulatory weight in 2026. The second and third rows carry most of the reputational weight. An LP rarely reads about a fund manager because an investor’s KYC file aged. It reads about one because a portfolio company CEO was charged, or because a placement agent was sanctioned.
For the investment-stage view of these relationships, our investment due diligence checklist covers pre-commitment checks. This guide covers what happens after the deal closes.
Why calendar-based reviews miss risk between cycles
A fixed review cycle creates a blind window. A high-risk relationship on a 12-month cycle can carry an undetected sanctions designation for up to 11 months. A low-risk service provider on a 3-year cycle can change owners twice before anyone looks.
The industry still leans on that model. In EY’s 2024 survey of global asset managers, 58% ran reviews on the traditional 1, 3 or 5-year cycle, and only 17% were purely event-driven.[3] IQ-EQ’s 2026 survey of more than 50 private markets fund managers found 48% still manage KYC through email and spreadsheets.[5]
Outsourcing moves the work, not the accountability
EY found 42% of asset managers outsource onboarding and KYC to third-party vendors.[3] IQ-EQ found 87% of larger managers use outsourced or hybrid KYC models.[5]
Each of those arrangements creates a service provider the manager now has to oversee. A firm that outsourced investor KYC to reduce work has, in regulatory terms, added a relationship that needs its own ongoing due diligence. Cayman’s 2026 rules say this outright.
Which regulations require ongoing due diligence from fund managers in 2026?
Four obligations are live now and fall directly on the manager’s third-party and portfolio relationships. Two more are dated horizons. The table separates what a rule requires from what is good practice.
| Rule | Date | What it asks of the manager | Status |
|---|---|---|---|
| CIMA AML Rule and Sanctions Rule (Cayman) | In force 18 Sep 2026 | Ongoing monitoring and sanctions screening; oversight of outsourced AML functions; independent AML audit covering third-party relationships and outsourcing | Live |
| SEC Regulation S-P amendments (17 CFR 248.30) | 3 Dec 2025 (larger); 3 Jun 2026 (smaller) | Written policies for due diligence on and monitoring of service providers with customer information access; 72-hour breach notice from those providers | Live |
| AIFMD II (Directive (EU) 2024/927) | Transposition 16 Apr 2026 | Stricter delegation and substance expectations for AIFMs overseeing delegates | Live (EU) |
| UK MLR 2017 as amended by SI 2026/621 | Most provisions 30 Jun 2026 | Ongoing monitoring under Reg 28(11); narrower bright-line EDD triggers, so more depends on documented judgement | Live (UK) |
| EU AMLR (Regulation (EU) 2024/1624) | Applies 10 Jul 2027 | Directly applicable CDD and ongoing monitoring rules across the EU | Horizon |
| FinCEN investment adviser AML/CFT rule (31 CFR 1032.210) | Postponed to 1 Jan 2028 | AML/CFT programme and SAR filing for RIAs and ERAs; FinCEN has said it intends to revisit the rule’s substance | Horizon |
Regulatory summaries are Neotas’ reading of published rules and law-firm guidance as of October 2026. They are not legal advice. Confirm scope for your fund structures with counsel.
United States: Regulation S-P is the clearest live trigger
For an SEC-registered adviser, Regulation S-P’s amended safeguards rule is the most concrete reason to formalise third-party monitoring now. Every adviser had to comply by 3 June 2026. The SEC’s Division of Examinations listed vendor oversight under Regulation S-P and S-ID, and operational resiliency, among its FY2026 priorities.[6]
One point is often misread. The SEC’s 2022 proposal on outsourcing by investment advisers was withdrawn on 12 June 2025. There is no standalone SEC outsourcing rule. The obligation comes through Regulation S-P, the adviser’s fiduciary duty and examination expectations.
The Corporate Transparency Act changed in the same period, in the opposite direction. FinCEN’s interim final rule of 21 March 2025 exempts US-formed companies and US persons from beneficial ownership reporting. Fewer filings mean ownership checks on US counterparties now depend more on independent investigation than on a registry.
Cayman: the trigger most US managers overlook
Many US sponsors run Cayman vehicles. CIMA’s AML Rule and Sanctions Rule apply to CIMA-registered funds, managers and advisers, and they took effect on 18 September 2026. Law-firm guidance on the rules states that outsourcing does not transfer accountability.[1] The independent AML audit has to examine third-party relationships and outsourcing, so the evidence of oversight is now something an auditor will ask to see.
UK and EU: portfolio monitoring already has a basis
The UK’s JMLSG guidance for private equity (Part II, Sector 13) says a private equity firm must conduct ongoing monitoring of its AML “customers”, which in some structures include portfolio companies. It accepts that board-level oversight can contribute to that duty.[7] In the EU, AIFMD II puts more weight on how an AIFM selects and supervises delegates.
Neotas, rated in the Chartis FCC50
See what your last review missed
Name up to five portfolio companies or service providers. A Neotas analyst runs them through OSINT, sanctions, adverse media and ownership checks and returns a sample ongoing due diligence report with its full audit trail.
What trigger events should prompt an out-of-cycle review?
A trigger list only works if it is tied to relationship type. A data breach at a fund administrator matters for Regulation S-P. The same event at a portfolio company is a value and reputation issue. The matrix below is Neotas’ working taxonomy, built from the regulatory obligations above.
| Trigger event | Portfolio company | Counterparty / co-investor | Administrator / delegate | Placement agent / distributor |
|---|---|---|---|---|
| Sanctions designation (direct or via 50% ownership) | Escalate | Escalate | Escalate | Escalate |
| Change in UBO or controlling shareholder | Review | Escalate | Review | Escalate |
| Key person departure, arrest or charge | Escalate | Review | Review | Escalate |
| Regulatory enforcement or licence action | Escalate | Review | Escalate | Escalate |
| Material litigation or insolvency signals | Review | Review | Escalate | Review |
| Credible adverse media (fraud, bribery, ML, labour, ESG) | Escalate | Review | Review | Escalate |
| Data breach or cyber incident | Review | Note | Escalate | Review |
| New PEP connection | Review | Escalate | Note | Escalate |
| Move into a higher-risk jurisdiction | Review | Review | Review | Escalate |
Escalate = analyst investigation and a documented decision within a set timeframe. Review = relationship owner reassesses the risk rating. Note = log against the file and consider at the next scheduled review.
Placement agents score high on most rows because they act in the manager’s name with investors, often across jurisdictions where the manager has no staff. Their risk is closer to an agent’s than a vendor’s.
How should a fund manager tier its third-party monitoring?
Tier by consequence, not by contract value. A low-fee distributor in a high-risk market can expose the manager more than a large technology vendor. Five factors decide most tiers:
Placement agents, distributors and finders speak to investors for you. Misconduct lands on the manager.
Administrators, transfer agents and technology vendors with customer information fall under Regulation S-P service provider oversight.
Outsourced AML, depositary and portfolio management delegation carry CIMA and AIFMD II accountability.
Layered holding structures, nominee directors and operations in higher-risk jurisdictions raise the tier.
Large positions and publicly visible portfolio companies carry more reputational exposure for the fund.
| Tier | Monitoring | Scheduled review | On trigger |
|---|---|---|---|
| Critical | Continuous: sanctions, adverse media in local languages, ownership, litigation | Annual enhanced review | Analyst investigation, documented decision |
| Significant | Continuous sanctions and adverse media | Every 2 years | Owner reassessment; escalate if confirmed |
| Standard | Continuous sanctions screening | Every 3 years | Owner reassessment |
Review frequencies are Neotas’ recommended starting point, not regulatory minimums. Set yours in your written risk methodology. Our enhanced due diligence checklist includes a monitoring-frequency-by-risk table you can adapt.
When does screening need investigation?
Screening tells you a name matched a list or an article. Investigation tells you whether it matters. Fund relationships produce three kinds of risk that database screening alone tends to miss.
- Hidden ownership. Sanctions exposure through a 50%-owned entity, or a co-investor’s backer sitting two layers up, does not appear as a direct list match. Ownership has to be traced through registries and open sources.
- Local-language media. The first report of a regulatory raid on a portfolio company in Brazil or Indonesia is usually in Portuguese or Bahasa, in regional outlets that many commercial adverse media feeds index late or not at all.
- Behavioural signals. Court filings, social media activity and changes in corporate filings show conduct that never reaches a watchlist.
This is where most programmes stall. They switch on continuous screening, alerts arrive, and nobody has the time or the method to resolve them. Unresolved alerts are worse than none, because an examiner can see the firm knew and did nothing.
What an ongoing due diligence report should contain
An ongoing due diligence report records what changed in a relationship and what the firm decided. At minimum it should hold the trigger and its source, the checks run, the findings with links to evidence, the analyst’s assessment, the risk rating before and after, the decision and its owner, and the date. That record is what CIMA’s independent auditor and an SEC examiner will ask for.
Our guide to adverse media screening covers why one-off screening and ongoing monitoring produce different results.
The Neotas Perpetual Due Diligence Maturity Model
Use these five levels to place your current programme. Each level scores two things: how many relationship types are covered, and what happens when something changes.
| Level | Coverage | Response to change |
|---|---|---|
| 1. Calendar | Investors only, at onboarding and fixed intervals | Found at the next review, if at all |
| 2. Screened | Investors and some counterparties rescreened automatically | Alerts generated, inconsistently resolved |
| 3. Mapped | All four relationship types inventoried and tiered | Defined trigger taxonomy and owners |
| 4. Investigated | Critical and significant tiers monitored continuously | Escalations go to analyst-led, multilingual investigation |
| 5. Evidenced | Whole relationship portfolio, on one dashboard | Every alert, finding and decision in an audit trail, mapped to the obligation it satisfies |
Our experience is that firms tend to overrate their level by one step. Continuous screening of investors feels like Level 4. Without a tiered inventory of portfolio companies and service providers, it is Level 2.
Common mistakes in fund manager third-party monitoring
- Treating the administrator’s KYC file as the whole programme. It covers investors. It says nothing about the administrator itself, your delegates or your portfolio.
- Relying on questionnaires for service provider oversight. A provider’s own answers describe its controls. They will not tell you about the enforcement action in its parent company’s home market.
- Stopping diligence at closing. Pre-deal checks on management teams are thorough at most sponsors. Post-close monitoring of the same people is often nobody’s job.
- Screening the entity, not its owners and officers. Many material events attach to a director or a beneficial owner, not the company name.
- Generating alerts without a resolution method. An unworked alert queue is evidence of a known, unaddressed risk.
Who owns perpetual due diligence: CCO, GC, COO and deal team
Each role meets this problem from a different direction. The programme works when each one knows which trigger is theirs.
Chief Compliance Officer
Your exposure is the exam or audit request: show Regulation S-P service provider oversight, show the CIMA outsourcing file. You need tiering logic and decision records, not just a vendor list.
General Counsel
Your exposure is the sanctions or enforcement event attached to a counterparty you contracted with. OFAC liability is strict, so the question is how fast you knew and what you did.
Chief Operating Officer
Your exposure is a critical provider failing or changing hands with no tested fallback. Ownership-change triggers on administrators and delegates belong on your dashboard.
Deal and portfolio teams
Your exposure is the portfolio company headline that reaches LPs before it reaches you. Key-person and adverse media triggers on management teams protect value and the next fundraise.
How Neotas supports perpetual due diligence
Neotas combines automated monitoring with analyst investigation, so alerts end in decisions. Each capability below maps to a problem described earlier.
| Problem | Neotas capability |
|---|---|
| Blind windows between reviews | Continuous monitoring across connected data sources, with custom alerting |
| Different risk across relationship types | Configurable risk models and dashboards by tier |
| Hidden ownership, local-language media | OSINT and social media intelligence, premium data sources and search in 30+ languages |
| Alerts that need judgement | Expert analyst team and enhanced due diligence reports |
| “Show me” from an examiner, auditor or LP | Full audit trail of every check, finding and decision |
Investment firms already use this approach. Coller Capital works with Neotas on OSINT-based ESG due diligence at the initial investment stage and for ongoing monitoring of the portfolio. Read how OSINT supports ESG due diligence for investors.
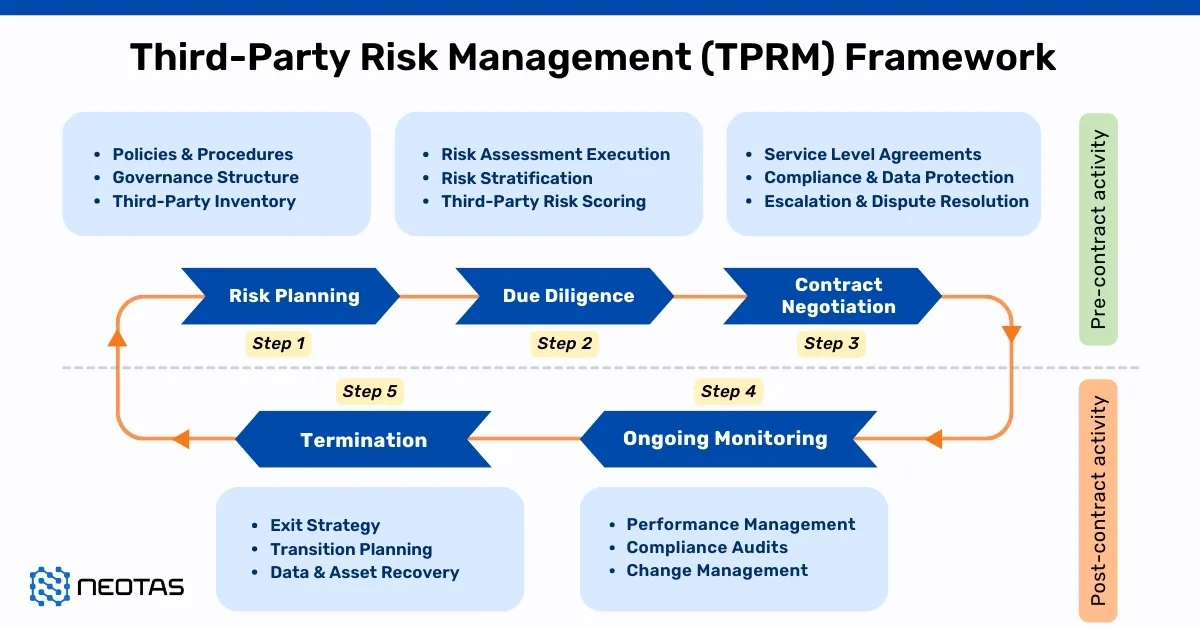
For the wider programme design, see our guide to third-party risk management and the TPRM lifecycle.
Ready for the next audit or exam request?
Score your programme against the Perpetual Due Diligence Maturity Model
If your third-party oversight still relies on questionnaires, onboarding checks and annual reviews, a 30-minute readiness assessment with a Neotas specialist will show where your portfolio companies and service providers sit outside your cycle, and what CIMA, Regulation S-P or AIFMD II evidence you are missing.
Related reading
Practical guides for fund compliance, legal and operations teams managing portfolio, counterparty and service provider risk.
Investment Due Diligence Checklist
The pre-commitment checks investors and managers run on funds, managers and service providers, including operational due diligence and the ILPA DDQ.
Private Equity Due Diligence Checklist
Buy-side checks on targets and management teams before closing, which set the baseline that post-close monitoring then tracks.
Enhanced Due Diligence Services
Analyst-led investigation for investment and operational due diligence on fund managers, portfolio companies and service providers.
Adverse Media Screening: What It Misses
Why keyword screening misses material media, and how ongoing adverse media monitoring differs from a one-off check.
Third-Party Risk Management Framework
How to structure risk tiering, due diligence depth by tier and governance for a third-party programme.
OSINT Due Diligence for Investors
How open-source intelligence exposes management and ownership risk that registry data and questionnaires do not show.
Due diligence on suppliers and service providers, from onboarding checks to the evidence a regulator expects to see.
Enhanced Due Diligence Checklist
EDD steps and an ongoing monitoring plan with review frequency by risk level and common trigger events.
Frequently asked questions: perpetual due diligence for fund managers
Answers based on regulatory sources and People Also Ask data for ongoing due diligence and perpetual KYC queries in US and UK search results.
Sources
[1] Cayman Islands Monetary Authority, AML Rule and Sanctions Rule, in force 18 September 2026; summarised in Walkers, “Cayman Islands new AML Rule and new Sanctions Rule: Practical Guide for Investment Funds”, August 2026.
[2] US SEC, Regulation S-P amendments (17 CFR 248.30), adopted May 2024; compliance dates 3 December 2025 and 3 June 2026.
[3] EY, “Asset management institutional client onboarding survey”, February 2024.
[4] Federal Register, FR Doc. 2025-24184, 2 January 2026.
[5] IQ-EQ, “KYC in private markets: Challenges, friction and the case for change”, March 2026 (updated June 2026).
[6] US SEC Division of Examinations, Fiscal Year 2026 Examination Priorities, November 2025.
[7] JMLSG Guidance Part II, Sector 13: Private equity, paras 13.78 to 13.79.
This article is for information only and does not constitute legal or regulatory advice.